 Hardware Ready Ready to Bench?
EvilTokens AI fraud platform. Microsoft has neutralized EvilTokens, a sophisticated AI-based cybercriminal platform. Launched in February 2026, the platform compromised over 12,000 email accounts across more than 10,000 global organizations, leveraging AI to orchestrate complex frauds ranging from access theft to target identification.
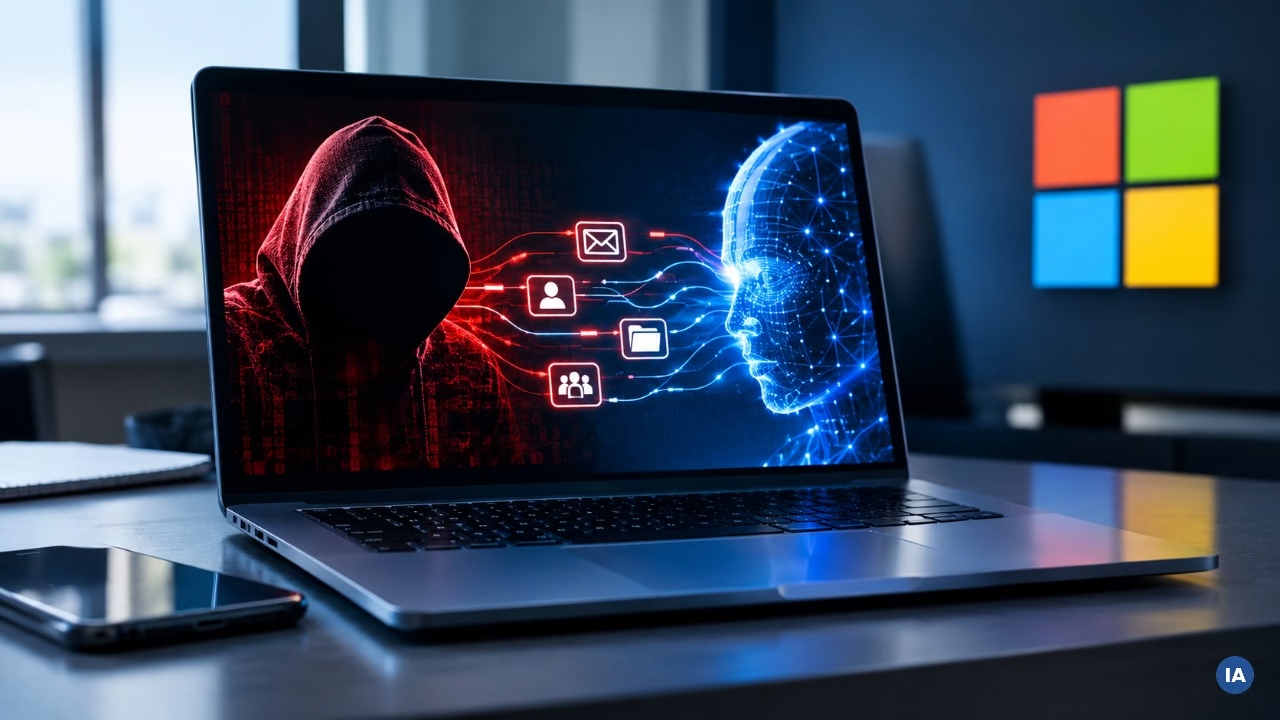
EvilTokens integrated artificial intelligence into every phase of the attack chain. An AI chatbot analyzed victims’ mailboxes, identifying trusted relationships, payment authorizations, and sensitive responsibilities to outline the most promising contexts for fraud. The AI suggested strategies and drafted deceptive messages to impersonate authoritative contacts.
EvilTokens AI fraud platform: why it matters
EvilTokens’ artificial intelligence precisely determined who to target, whom to impersonate, and how best to exploit relationships to maximize illicit gains. The service quickly gained traction, compromising over 12,000 email accounts in more than 10,000 organizations worldwide.
The highest concentrations of victims were recorded in the United States, Canada, the United Kingdom, Australia, India, and France, with affected sectors ranging from distribution to construction, financial services to higher education and healthcare. The access mechanism relied on deceiving victims into entering an authentication code on Microsoft’s legitimate login page.
This allowed criminals to access email accounts without stealing passwords, with access that could persist even after a password reset if associated sessions and tokens were not revoked. Microsoft Threat Intelligence provides technical details on these operations and so-called device-code attacks, urging users to adopt protective measures.
Traditionally, it took criminals time and experience to scan thousands of messages, identify decision-makers, understand payment processes, and uncover fraud opportunities. EvilTokens automated this process: its AI tools could summarize and translate emails, highlight financial conversations, map organizational roles, identify trust relationships, and recommend potential targets.
Preset prompts allowed users to locate discussions about wire transfers, identify “money movers” (those who handle funds), find supplier invoices, and determine the best individuals to impersonate. The service was sold via Telegram with an initial fee of $1,500 and a recurring subscription of $500.
What changes and what are the effects
The takedown operation is the result of coordinated action between Microsoft, law enforcement agencies, and industry partners such as Health-ISAC, Cloudflare, Coinbase, OpenAI, and others. Microsoft seized 50 websites and disabled over 150 domains linked to the support infrastructure.
In the United Kingdom, Metropolitan Police arrested two men aged 32 and 38 on September 11 in connection with the EvilTokens operation. This intervention marks the fortieth court-authorized takedown by Microsoft’s Digital Crimes Unit (DCU) and the first against an end-to-end AI-enabled cybercrime service.
Microsoft warns that while the infrastructure has been dismantled, the attack model does not disappear with it. Increasingly capable and accessible AI is being used to scale fraud, impersonation, and other forms of online abuse. Organizations must therefore assume that a compromised email account can be analyzed by criminals in minutes, not days.
Robust identity protections and monitoring remain essential, but it is also crucial to independently verify requests for payment information changes, fund redirections, or approvals of unusual transactions via a second trusted channel.
Source and further reading on EvilTokens AI fraud platform: original article.
* Content created with the assistance of artificial intelligence systems.