 Hardware Ready Ready to Bench?
malicious PEC campaign. CERT-AGID has countered an ongoing campaign that exploits compromised Certified Electronic Mail (PEC) accounts to send harmful messages to other certified email addresses. The messages, which began circulating on the evening of September 23, appear as fake reminders for unpaid invoices, intending to induce recipients to quickly settle their debt positions.
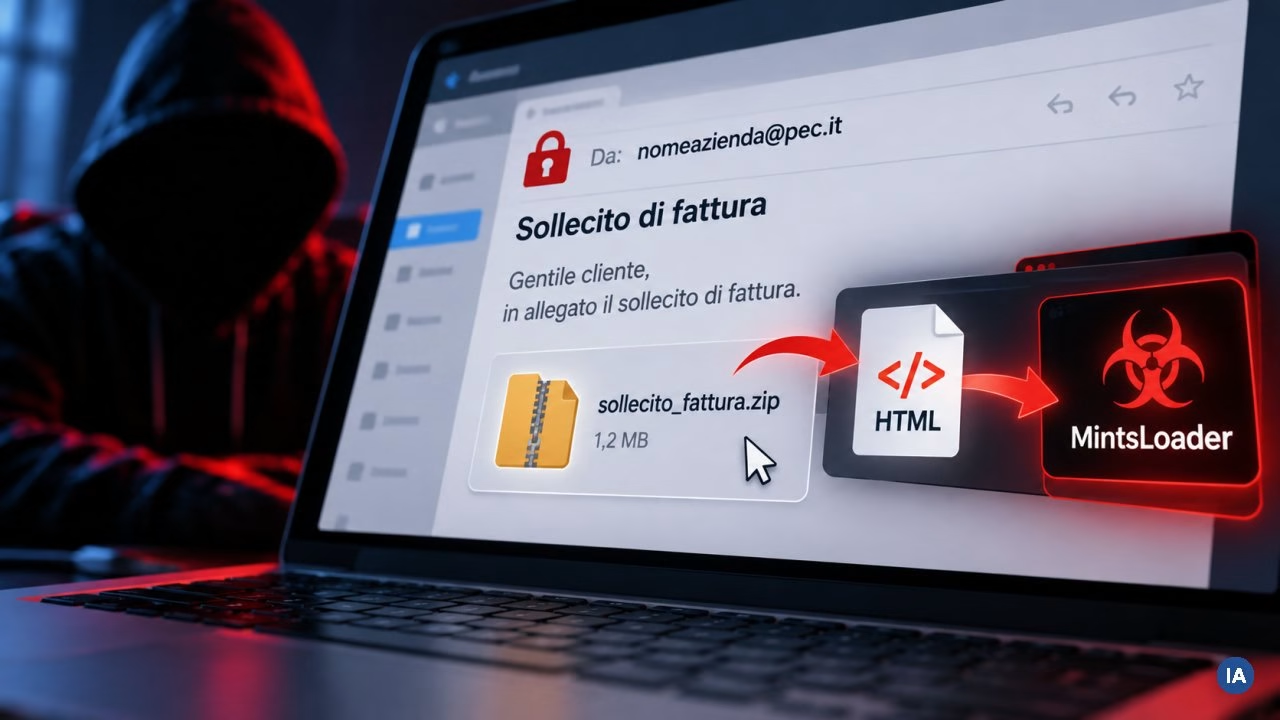
According to CERT-AGID’s analysis, the preparation of the campaign appears to have started on Monday, September 21. The messages originate from real PEC accounts, but the agency emphasizes that Certified Electronic Mail guarantees only the transmission and delivery of the message, without certifying the integrity of the sender’s mailbox or the security of attachments.
malicious PEC campaign: why it matters
The subject lines of the messages vary frequently to evade filtering systems, including examples such as “Reminder for overdue invoice payment,” “Pending invoice reminder,” and various variants concerning unpaid invoices or accounting irregularities. The primary objective is to push the recipient to open the attachment.
Each PEC contains a ZIP archive, named in a way that evokes an invoice or administrative document. Inside the archive is an HTML file which, once opened, establishes a connection with infrastructure controlled by the attackers and downloads a JavaScript script. This script is executed via standard Windows operating system components and initiates further execution phases based also on PowerShell.
The infection chain culminates in the execution of MintsLoader, a malicious loader responsible for downloading and executing other harmful software on the compromised system. In this case, the installed malware consists of RATs (Remote Access Trojans) or infostealers, designed to steal sensitive information.
The addresses used to retrieve the various malicious components change frequently and also exploit Domain Generation Algorithm (DGA) techniques, already observed in previous campaigns that utilized MintsLoader. In the first hours after sending, the domains contained in the files analyzed by CERT-AGID were inactive, becoming operational only on the morning of September 24.
What changes and what are the effects
CERT-AGID had already encountered this pattern in previous campaigns, noting that domains are activated during working hours when messages are already present in recipients’ mailboxes. CERT-AGID therefore initiated countermeasures with the support of PEC providers and shared indicators of compromise (IoC) via its feed with accredited structures to allow for the timely blocking of the infrastructure and artifacts used. The same IoCs were made public along with the bulletin.
Therefore, it is recommended to treat unexpected PECs regarding invoices, payments, or reminders with extreme caution, especially if they contain ZIP archives, even when the sender appears legitimate. CERT-AGID also invites users to forward suspicious communications for thorough verification.
Source and further reading on malicious PEC campaign: original article.
* Content created with the assistance of artificial intelligence systems.